

Blog
How to Proxy Only www Through Cloudflare While Keeping CloudFloorDNS as Your DNS
October 8, 2026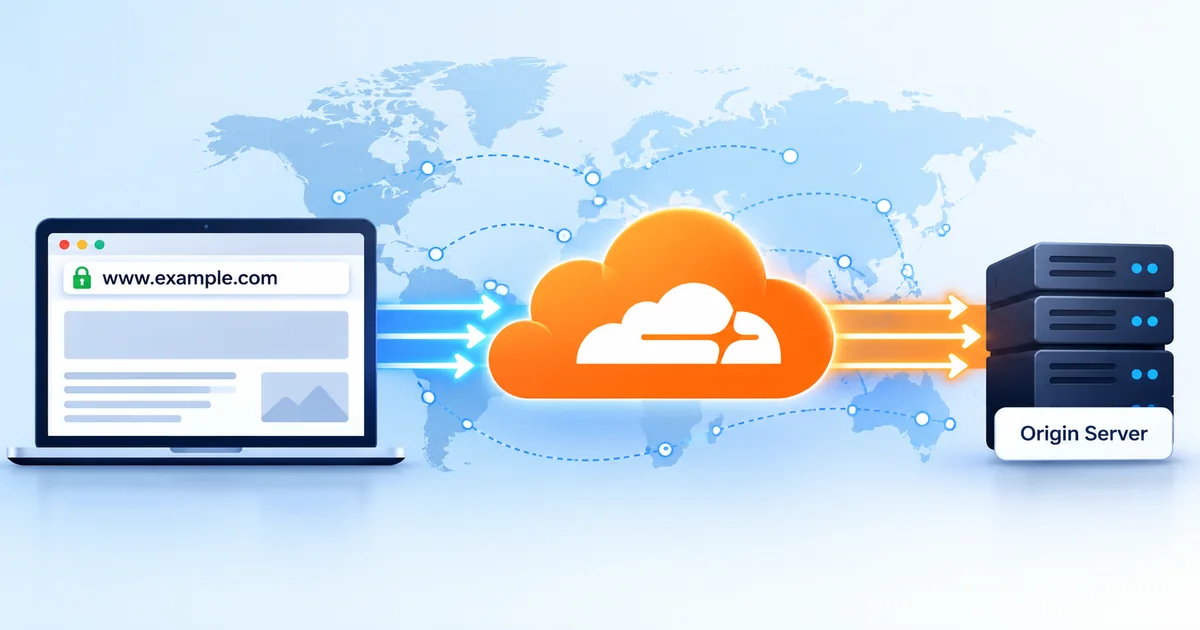
Cloudflare’s reverse proxy is a popular way to put a CDN, a web application firewall and DDoS protection in front of a website. The catch is the onboarding: Cloudflare’s standard setup asks you to move your nameservers, which hands over your entire DNS zone — mail, verification records, VPN and API hostnames included — just to protect one website.
You don’t have to. On its Business and Enterprise plans, Cloudflare supports a CNAME setup (its documentation also calls it a partial setup): your authoritative DNS stays where it is, and you point only the hostnames you want proxied at Cloudflare. This guide walks through doing that for www, with CloudFloorDNS staying in charge of everything else.
The short version
Add your domain to Cloudflare on a Business or Enterprise plan and convert it to a CNAME setup. Prove ownership with a TXT record at CloudFloorDNS, create a proxied www record in Cloudflare and get its certificate validated, then turn www at CloudFloorDNS into a CNAME pointing at www.example.com.cdn.cloudflare.net. Your nameservers never change.
Why keep your DNS at CloudFloorDNS?
Cloudflare is good at what it does, and so is a dedicated DNS provider. Splitting the jobs gets you a few things an all-Cloudflare setup can’t:
- Everything else keeps resolving from the network you chose for it. MX, SPF, DKIM, DMARC, VPN, VoIP and API records never pass through Cloudflare.
- You keep your DNS tooling. DNS Failover, GeoDNS, Secondary DNS, one-click DNSSEC and our API keep working for everything you don’t send to Cloudflare.
- The off switch isn’t inside the thing you’re switching off. If Cloudflare’s proxy has a bad day, you can send visitors straight to your server with one record change at CloudFloorDNS — more on that below.
- Leaving is easy. Dropping Cloudflare later is a single DNS edit, not a nameserver migration.
How a Cloudflare CNAME setup works
A visitor’s resolver asks CloudFloorDNS for www.example.com. We answer with a CNAME to www.example.com.cdn.cloudflare.net.
That name resolves to Cloudflare’s anycast network, where the request meets the cache, the WAF and Cloudflare’s DDoS protection.
Anything Cloudflare can’t serve from cache is fetched from your origin, at the address you give Cloudflare in Step 4.
The bare domain, mail and every other hostname are answered by CloudFloorDNS as usual and go direct. Cloudflare never sees them.
Things worth knowing before you start
The details a sales page usually leaves out:
It needs Cloudflare Business or Enterprise.
The CNAME setup isn’t offered on Free or Pro — the conversion option simply doesn’t appear. Cloudflare lists Business at $200/month billed annually or $250/month billed monthly (current plans).
The bare domain can’t be a CNAME.
DNS doesn’t allow a CNAME at the zone apex, so example.com can’t point at Cloudflare the way www does. You’ll send it to www instead; Step 8 covers the options.
Only what you point at Cloudflare is proxied.
Cloudflare handles exactly the hostnames you CNAME to it. That includes DNS itself: Cloudflare’s DNS-layer DDoS protection only applies when it runs your nameservers, so here your DNS stays on CloudFloorDNS’s DDoS-protected network.
Your origin address moves into Cloudflare.
After the switch, the www record in Cloudflare’s dashboard decides where traffic goes. When you move servers, update it there, not at CloudFloorDNS.
Some records are permanent.
Cloudflare’s cloudflare-verify TXT record has to stay in your zone for as long as you use the setup, and so does the _acme-challenge CNAME if you choose delegated certificate validation in Step 5.
Cloudflare Registrar domains are excluded.
Domains registered at Cloudflare can’t use a CNAME setup. Registered with us or with any other registrar? You’re fine.
Step-by-step: proxy www through Cloudflare
Throughout this guide, example.com stands in for your domain and 203.0.113.10 for your web server’s IP address. Each step is labeled with where you’ll be working.
Note your current www record and lower its TTL
Open the zone for example.com in the CloudFloorDNS control panel and find the www record. Write down its value: that’s your origin, and it’s also your way back. Then lower its TTL to 600 seconds (10 minutes) and wait at least as long as the old TTL before you continue, so the change in Step 7 takes effect quickly.
If www is already a CNAME to a hosting provider (something like yoursite.hostingco.net), note that hostname instead. You’ll use it as the origin in Step 4.
Add the domain and convert it to a CNAME setup
Add example.com to your Cloudflare account and choose the Business (or Enterprise) plan. Cloudflare scans your existing records and then tells you to change your nameservers. Ignore the nameserver instructions.
On the domain’s Overview page, select Convert to CNAME DNS Setup and confirm with Convert. Cloudflare then shows a Verification TXT Record. Copy it; if you lose it, it’s also listed on the DNS Records page.
Prove you own the domain
Add the verification record to your zone:
| Name | Type | Data | TTL |
|---|---|---|---|
cloudflare-verify |
TXT | The value Cloudflare shows you, e.g. 966215192-518620144 |
3600 |
Type just cloudflare-verify in the name column; the panel adds your domain for you. Cloudflare checks for the record and emails you when the zone is active, which can take up to a few hours. To confirm the record is being served:
dig +short TXT cloudflare-verify.example.comLeave this record in place permanently. Cloudflare uses it to keep confirming you control the zone.
Create the proxied www record
Go to DNS → Records and make sure there’s a record for www pointing at your origin, with the proxy turned on (orange cloud, Proxied):
| Type | Name | Content | Proxy status |
|---|---|---|---|
| A | www |
203.0.113.10 |
Proxied |
| AAAA (only if your server has IPv6) | www |
2001:db8::10 |
Proxied |
If your host gives you a hostname rather than an IP address, create a proxied CNAME for www pointing at that hostname instead. Don’t point it at anything that resolves back through Cloudflare, such as your bare domain.
Then delete everything else the scan imported. Cloudflare isn’t answering DNS for your domain in this setup, so those copies do nothing for visitors, and if a proxied CNAME ever points at one of them, Cloudflare uses its own stale copy instead of asking CloudFloorDNS. Keep this zone to the hostnames you proxy.
Get the edge certificate issued before you switch
Cloudflare includes a free Universal SSL certificate, but on a CNAME setup it can’t validate the certificate automatically until traffic is already flowing through Cloudflare — unless you add validation records at your DNS provider first. Switch DNS before the certificate is active and HTTPS visitors can see certificate errors until it completes; Cloudflare’s own documentation says HTTP validation is only for sites that can tolerate a few minutes of downtime. For a live site, validate through DNS first. There are two ways:
Recommended for live sitesAdvanced certificate with delegated validation
Add Advanced Certificate Manager (listed at $10/month) and order an advanced certificate for example.com and *.example.com, choosing TXT as the validation method. Then, on SSL/TLS → Edge Certificates, find DCV Delegation for Partial Zones, copy the validation URL and add one record at CloudFloorDNS:
| Name | Type | Data |
|---|---|---|
_acme-challenge |
CNAME | example.com. followed by the validation URL Cloudflare shows, ending in a dot |
From then on Cloudflare validates and renews on its own, and the wildcard covers any other hostname you proxy later. Two things to know: remove any existing _acme-challenge TXT records first, because they block delegation; and since only one provider can hold the delegation, DNS-based certificate validation for the same names elsewhere (a certbot DNS plugin on your server, for example) stops working. HTTP-based validation isn’t affected.
No extra costUniversal SSL, validated with a TXT record
Check SSL/TLS → Edge Certificates. If a pending Universal certificate for www lists a certificate validation TXT name and value, add that TXT record at CloudFloorDNS (the name will look like _acme-challenge.www). If it’s set to a different method, switch it to TXT; for Universal certificates Cloudflare only allows that through its API. You’ll need your zone ID (on the Overview page) and an API token with the SSL and Certificates: Edit permission for the zone:
CF_API_TOKEN="your-api-token"
ZONE_ID="your-zone-id"
API="https://api.cloudflare.com/client/v4/zones/$ZONE_ID"

# 1. Find the Universal certificate pack that covers www
curl -s "$API/ssl/certificate_packs?status=all" \
  -H "Authorization: Bearer $CF_API_TOKEN" \
  | jq '.result[] | {id, type, hosts, status}'

# 2. Switch that pack to TXT validation
CERT_PACK_ID="id-from-step-1"
curl -s -X PATCH "$API/ssl/verification/$CERT_PACK_ID" \
  -H "Authorization: Bearer $CF_API_TOKEN" \
  -H "Content-Type: application/json" \
  --data '{"validation_method":"txt"}'
Once the certificate shows Active, you can delete the TXT record. At renewal time (30 days before expiry) Cloudflare tries HTTP validation automatically; if that can’t complete, it falls back to TXT and you’ll need to add fresh values from Edge Certificates. The delegated route above avoids that chore entirely.
If no certificate is listed at all, Cloudflare issues it after traffic starts arriving. In that case, make the Step 7 switch at a quiet hour and expect a few minutes of certificate errors for HTTPS visitors.
Use Full (strict) and test before you switch
Under SSL/TLS → Overview, make sure the encryption mode is Full (strict), so Cloudflare connects to your server over HTTPS and checks its certificate. If the zone uses Automatic SSL/TLS, it picks the most secure mode your origin supports; choose Custom to set it yourself. Avoid Flexible: it leaves the Cloudflare-to-server leg unencrypted and causes redirect loops on sites that already force HTTPS.
You can now send a request through Cloudflare without touching DNS:
# Pin www.example.com to a Cloudflare edge address for this one request
CF_IP=$(dig +short www.example.com.cdn.cloudflare.net | head -n1)
curl -sI --resolve www.example.com:443:$CF_IP https://www.example.com \
  | grep -iE '^(HTTP|server|cf-ray)'
You’re looking for a normal status code, server: cloudflare and a cf-ray header. A TLS error means the edge certificate isn’t active yet (on the quiet-hour route from Step 5, add -k to test everything else). A 5xx error means Cloudflare can’t reach your server, so check the address from Step 4 and your firewall.
Point www at Cloudflare
Change the www record from its A/AAAA value into a CNAME:
| Name | Type | Data | TTL |
|---|---|---|---|
www |
CNAME | www.example.com.cdn.cloudflare.net. |
600 |
Keep the trailing dot: the target is outside your zone, so it’s entered as a full name ending in a dot. A CNAME can’t share its name with other records, so remove anything else at www too, such as an AAAA record or an old TXT verification record.
Make it one edit, not two.
Turn the existing www row into the CNAME (or add the CNAME and remove the old records in the same save) rather than deleting first and coming back later. A resolver that asks while www doesn’t exist can cache “no such name” for your zone’s negative-caching time.
Within roughly the TTL you set in Step 1, visitors to www are flowing through Cloudflare.
Send the bare domain to www
Because example.com can’t be a CNAME, decide what happens when someone types it. In order of preference:
- Redirect it at CloudFloorDNS. Add an REDIRECT:// record with the name left blank and
https://www.example.comas the data. Our forwarding servers answer for the bare domain and send visitors to www, so your server’s IP doesn’t appear on the bare domain at all. An aux value of 10 keeps the path (example.com/pricing→www.example.com/pricing); once you’ve tested it, 12 makes it a permanent 301. For visitors who typehttps://in front of the bare domain, the forwarder also needs a certificate for it: our Secure Branding and Forwarding plans include automatic Let’s Encrypt certificates, or ask support what your plan covers. - Proxy it through Cloudflare too. Cloudflare can proxy the apex in a CNAME setup when your DNS provider can flatten it, which is what an ALIAS record does. Add an ALIAS record with the name left blank pointing to
example.com.cdn.cloudflare.net., add a proxiedexample.comrecord in Cloudflare, and create a Redirect Rule there that sends it to www. Make sure your edge certificate coversexample.comas well. - Redirect on your own server. Keep the apex A record pointing at your server and redirect to www there. It’s the simplest option, but it publishes your server’s IP, sends bare-domain visitors around Cloudflare, and stops working if you lock your server down to Cloudflare’s addresses in Step 10.
Verify everything
# Ask your authoritative nameservers directly
NS=$(dig +short NS example.com | head -n1)
dig +short www.example.com CNAME @$NS   # expect www.example.com.cdn.cloudflare.net.
dig +short MX example.com @$NS          # unchanged

# Requests to www should come back from Cloudflare
curl -sI https://www.example.com | grep -iE '^(server|cf-ray)'

# The bare domain should redirect to www
curl -sI https://example.com | grep -i '^location'
Then check mail flow and any other hostnames you care about. They should behave exactly as before, because nothing about them changed.
Lock down the origin and log real visitor IPs
Cloudflare only protects traffic that goes through it. Anyone who learns your server’s address can still reach it directly, so finish with three checks:
- Accept web traffic only from Cloudflare. Restrict ports 80 and 443 to Cloudflare’s published IP ranges, or turn on Authenticated Origin Pulls so your server only accepts connections that present Cloudflare’s client certificate.
- Look for records that give the address away. Hostnames such as
ftp,cpanelordirectthat point at the same server publish its IP. Move those services or accept the exposure knowingly. - Restore visitor IPs in your logs. Your server now sees Cloudflare’s addresses. Cloudflare passes the original visitor IP in the
CF-Connecting-IPheader; configuremod_remoteip(Apache) or thereal_ipmodule (nginx) to trust that header from Cloudflare’s ranges only.
Your escape hatch when Cloudflare has a bad day
This is the quiet advantage of keeping DNS at CloudFloorDNS. On November 18, 2025, Cloudflare’s network failed to deliver core traffic for roughly three hours, and for parts of the incident most customers couldn’t log in to the Cloudflare dashboard (Cloudflare’s postmortem). When your nameservers are at Cloudflare, the controls you’d use to route visitors around it are part of the same platform. With CloudFloorDNS, it’s one record:
| Situation | Name | Type | Data |
|---|---|---|---|
| Normal | www |
CNAME | www.example.com.cdn.cloudflare.net. |
| Cloudflare outage | www |
A | 203.0.113.10 |
For that switch to work when you need it:
- Your server needs a publicly trusted certificate, such as one from Let’s Encrypt. A Cloudflare Origin CA certificate is only trusted by Cloudflare, so browsers would reject it the moment you bypass.
- Your firewall has to let visitors in. If you limited ports 80 and 443 to Cloudflare in Step 10, keep a ready-made rule to open them.
- Keep the www TTL modest. Somewhere around 10 to 30 minutes balances DNS query volume against how quickly the switch takes hold.
- Your server will be on its own, with no CDN cache and no Cloudflare WAF until you switch back, so make sure it can carry the load.
Rather not make that change by hand in the middle of the night? Our DNS Failover service can monitor the site and switch records for you; ask us about setting it up for a Cloudflare-fronted hostname.
Records at a glance
When you’re done, this is where everything lives:
| Where | Name | Type | Value | Notes |
|---|---|---|---|---|
| CloudFloorDNS | cloudflare-verify |
TXT | From Cloudflare | Keep permanently |
| CloudFloorDNS | www |
CNAME | www.example.com.cdn.cloudflare.net. |
Replaces the old A/AAAA |
| CloudFloorDNS | _acme-challenge |
CNAME | example.com. plus Cloudflare’s validation URL |
Delegated validation only; keep permanently |
| CloudFloorDNS | _acme-challenge.www |
TXT | From Cloudflare | Universal + TXT only; delete once issued |
| CloudFloorDNS | (blank) | REDIRECT:// or ALIAS | https://www.example.com or example.com.cdn.cloudflare.net. |
See Step 8 |
| CloudFloorDNS | MX, SPF, DKIM, DMARC, everything else | — | Unchanged | Never touches Cloudflare |
| Cloudflare | www |
A / AAAA, proxied | 203.0.113.10 |
Your origin; update it here when you move servers |
Frequently asked questions
Does my email go through Cloudflare?
No. MX, SPF, DKIM and DMARC records stay at CloudFloorDNS and resolve directly. Only hostnames you CNAME to Cloudflare are proxied.
Can I proxy other hostnames later?
Yes. Repeat Steps 4 through 7 for each one (shop or app, say): add a proxied record in Cloudflare, make sure the certificate covers it, then CNAME it to shop.example.com.cdn.cloudflare.net. at CloudFloorDNS. The wildcard advanced certificate from Step 5 covers new subdomains automatically.
What happens to DNSSEC?
Nothing changes. Your zone stays signed at CloudFloorDNS, and the www CNAME is signed along with everything else. Cloudflare doesn’t need your keys or a DS record in a CNAME setup.
I’m on Cloudflare Free or Pro. What are my options?
Cloudflare only offers the CNAME setup on Business and Enterprise, so on Free or Pro the proxy comes with moving your nameservers. If you go that way, plan for redundancy: a classic secondary behind Cloudflare depends on Cloudflare’s outgoing zone transfers, which it limits to Enterprise. We can talk you through a dual-primary alternative.
How do I undo it?
Change www at CloudFloorDNS back to an A record pointing at your server. Once the TTL passes, traffic goes direct again, and you can remove the domain from Cloudflare along with the cloudflare-verify and any _acme-challenge records.
Related guides
- Secondary DNS with Cloudflare as your primary
- DNS Failover: monitor and fail over to a backup IP or CNAME
- Secure Branding and Forwarding: HTTPS redirects with automatic certificates
- Why use a secondary DNS provider?
Keep your DNS independent. Put Cloudflare where it helps.
CloudFloorDNS is run by a team with more than 25 years in DNS, on a DDoS-protected network backed by a 100% uptime SLA. Keep your zone with us, proxy the hostnames that benefit, and keep control of everything else.
Questions about a Cloudflare CNAME setup? Email support@cloudfloordns.com or sales@cloudfloordns.com, or call +1 781 373 5823.